
The Cyber Police of Ukraine have warned of a new fraud scheme in which perpetrators distribute malicious applications disguised as free offline navigation apps that can gain access to users’ personal data and banking services.
According to the Cyber Police, potential victims are offered a navigation app that supposedly works without an internet connection, contains no advertising and is available free of charge. Advertisements for such applications are distributed primarily through social media.
After clicking on an advertisement, users are redirected to a third-party website where they are offered a program to download, including through a Telegram bot. Instead of the advertised navigation app, a malicious file may be installed on the smartphone.
During installation, the program requests permission to download applications from unknown sources, as well as access to certain smartphone functions. After obtaining these permissions, perpetrators can track the device owner’s actions, intercept messages and notifications, and obtain confidential information.
The malicious program’s access to SMS messages and system notifications poses a particular threat. The information obtained may be used to intercept verification codes and access the user’s accounts and financial services.
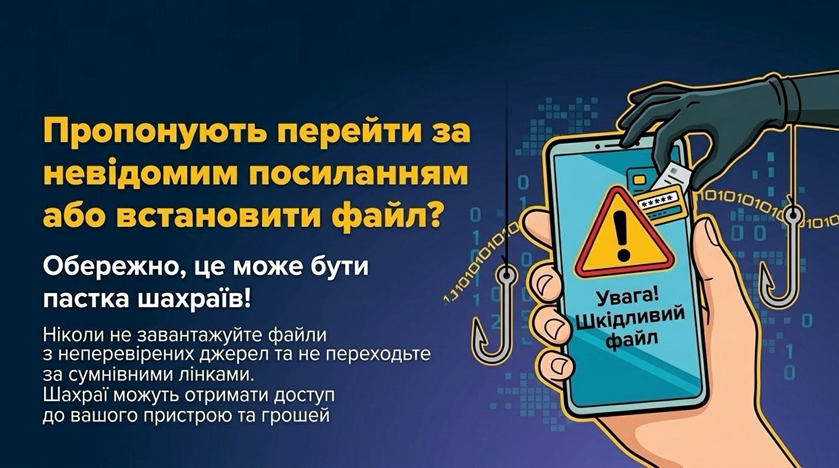
The Cyber Police recommend installing mobile applications exclusively from the official Google Play and App Store marketplaces and not downloading APK files through Telegram bots, unknown websites or advertising links.
Users are also advised to carefully check the permissions requested by an application. In particular, a navigation program should not gain access to SMS messages, notifications or device management functions without an objective need.
If a suspicious application has already been installed, specialists recommend temporarily refraining from using banking and other critically important services on that smartphone, disconnecting the device from the internet and changing the passwords for primary accounts from another secure device.
The suspicious program should be removed, and the permissions granted to it should be checked. If the application cannot be removed or continues to run in the background, seeking technical assistance is recommended.
If banking details have been disclosed or unknown transactions appear, users must immediately contact their bank to block possible unauthorized access to their accounts. Cases of fraud can be reported to the Cyber Police through their official online form.
The Cyber Police also recommend checking information about current fraud schemes on the government platform StopFraud.
Source: Cyber Police of Ukraine
APPLICATION, BANK, CYBER POLICE, CYBERSECURITY, fraud, smartphone
Scammers in Ukraine use ads for passenger and freight transportation to obtain advance payments by creating fake pages for private carriers and logistics companies.
To build trust, the scammers use photos of real buses and trucks, logos of well-known companies, reviews from other people, and other copied materials. Potential customers are usually lured in by lower travel or delivery costs compared to market rates.
Once a customer contacts them, the scammers try to get the money as quickly as possible. In particular, they may claim that there are almost no seats left or that an advance payment must be made immediately to confirm the reservation.
When arranging freight transportation, scammers may demand full payment in advance via a credit card or to an individual’s bank account. After receiving the money, the fake carrier stops responding, and the ad or page is deleted. In some cases, after the first transfer, the customer is asked to make additional payments supposedly for insurance, documents, customs clearance, or other services.
Experts cite the following as signs of potential fraud: a significantly low price, a demand for an urgent prepayment, communication exclusively via messaging apps, recently created carrier pages, and a lack of operational history. The risk also increases if the carrier refuses to provide detailed information about the route, vehicle, and terms of transport, or demands new payments after an agreement has been reached.
Links for booking and payment pose a particular danger. They may lead to phishing sites that mimic the appearance of banking and payment services. Their purpose is to obtain bank card details and other payment information.
Users are advised to verify the company name and phone number through several independent sources before making a payment, review the carrier’s reviews and track record, and avoid sharing CVV codes, passwords, or one-time transaction confirmation codes.
If money has already been transferred to scammers, it is recommended to save the correspondence, screenshots of the ad, and payment confirmation. If you have disclosed your banking information, you should contact your bank as soon as possible. You can also report cases of fraud to the Cyber Police or by calling 102 or 112.
You can learn more about current fraud schemes and ways to protect yourself on the StopFraud platform.
Ukraine’s Cyber Police have warned citizens about a scam involving fake electricity bills, which may be sent via email or messaging apps purportedly on behalf of the Ministry of Energy or other government agencies.
According to the statement, scammers may inform recipients of alleged outstanding balances, send payment invoices, or demand immediate payment. To make their messages more convincing, they use official logos, the names of government agencies, and formatting that resembles genuine communications.
The main goal of the attackers is to trick users into clicking a link to a phishing website. There, they may be asked to enter their credit card information, username, password, SMS verification code, or other personal information. Malware may also be distributed under the guise of a bill or document. As a result, scammers can gain access to bank accounts, email, social media, and other accounts.
The Cyber Police emphasize that the Ministry of Energy of Ukraine does not send electricity bills to consumers and does not collect utility payments. Bills are issued directly by the electricity suppliers with whom consumers have signed contracts.
Signs of a fraudulent message may include a demand for immediate payment via a link provided, information about a non-existent debt, a sender’s email address that does not belong to an official institution, a request to enter bank details or a password, as well as unknown attached files.
Grammatical errors, unusual phrasing, and attempts to create a sense of urgency should also raise red flags.
It is recommended to verify information about electricity payments only through your provider’s official website or app. The cyber police advise against clicking on links in suspicious emails and against entering personal or banking information on websites linked to via email or messaging apps.
If a user has already clicked on a suspicious link, entered banking information, or lost funds, they should contact their bank as soon as possible to block their payment instruments. It is also important to save the correspondence, links, phone number, and other evidence to report the incident to law enforcement.
Additional information about current fraud schemes and ways to protect yourself can be found on the “Cyber Brama” portal at stopfraud.gov.ua.
16 billion current passwords leaked online, including access to Apple, Google, and Facebook
According to Forbes, researchers from Cybernews have recorded a unique leak — more than 16 billion current login and password pairs on sites including Apple, Google, Facebook, and other services.
This is the largest leak in history: 30 different databases, each containing tens of millions to 3.5 billion records. About 184 million accounts from previous leaks were already known, while the rest is new, “fresh” and vulnerable information.
The data is suitable for instant phishing attacks and account hacks — the login-password structures are ready to use. These are not old leaks, but new, fresh lists that are actively being sold on dark forums.
What experts advise:
• Change passwords for all important online accounts (Google, Apple, social networks, email, etc.).
• Enable two-factor authentication (2FA) — via SMS, code generator app, or hardware keys.
• Switch to passkeys — password-less logins protected by biometrics or PINs, recommended by Google and Meta.
• Use a password manager to generate long, unique combinations and store them securely.
• Do not click on links from unverified SMS messages, emails, or messengers to avoid phishing.
Even old passwords (even “12345678”) are still relevant — they are often used in such leaks. After leaks, many people do not change them in time: according to research, only ~33% of users update their password after an incident — and only 13% do so within 3 months.
Recorded Future, the world’s largest private intelligence and analytical company, will continue to support Ukraine in 2024 by allocating more than $23 million for Ukraine’s cybersecurity, Deputy Prime Minister for Innovation, Education, Science and Technology Development and Minister of Digital Transformation Mykhailo Fedorov said on Monday.
“Recorded Future tools help detect and eliminate cyberattacks at an early stage. These tools are used by the Ministry of Digital Transformation, the State Special Communications Service, the GUR, the SBU, the Ministry of Defense, the Prosecutor General’s Office and the Cyber Police,” Fedorov wrote on his Telegram channel.
According to him, the company also works with key enterprises in the energy and telecom sectors.
As reported, Recorded Future provided intelligence to protect Ukraine’s critical infrastructure, assisted in the investigation of Russian war crimes, and opened access to the Intelligence Cloud software platform.
In total, in 2023, the company invested more than $20 million in assistance to Ukraine.
As part of the Ukrainian-African renaissance, Ukraine seeks to develop relations of mutual respect and benefit with African countries, in particular offering a number of beneficial areas of cooperation for Nigeria’s new leadership, Ukrainian Foreign Minister Dmitry Kuleba said in an interview with the Nigerian edition of The Guardian Nigeria.
“In May, I became the first Ukrainian foreign minister to attend the presidential inauguration ceremony in an African country. It was Nigeria. This fact shows Ukraine’s commitment to developing relations with Nigeria’s new leadership. This way we show other African countries that Ukraine seeks to develop partnership based on mutual respect and shared benefits,” he said, according to the press service of the Ukrainian Foreign Ministry.
According to Kuleba, Ukraine has made steps towards each other in the spirit of mutual respect and now counts on reciprocal steps of the new leadership of Nigeria to develop mutually beneficial relations.
“We propose to increase the volume of trade and consider the possibility of attracting Ukrainian construction companies to projects in Nigeria. Ukraine also has a lot of experience in digitalization. Our “State on Smartphone” program allows citizens to do almost everything online, receive public services. We are ready to share this experience with you. Another promising area of cooperation is cybersecurity. Nigeria is one of the countries that suffer from the highest number of cyber attacks. We know how to counter them effectively,” he said.
Kuleba also stressed that the Peace Formula proposed by Ukrainian President Vladimir Zelensky is the only real way to restore a just and sustainable peace in Ukraine.
“Imagine if Nigeria, God forbid, experienced aggression – would you agree to give up part of your territory, allow someone to occupy it and torture your people? You wouldn’t agree to that. Being at the inauguration of your president, I saw your army. I am convinced that your warriors would have fought resolutely for your land. That is what we are doing today. We did not start this war. The hostilities are taking place on our territory, but we know what we are fighting for: the freedom and security of our citizens. And that motivates us to fight against the invaders,” the minister said.



